Sorry to hear that. I had a quick look and both the 2022 version and the 2024 version of QD4 have Secure Boot. However, there is no TPM support. My questions:
Do you have a complete 16M copy of the original BIOS still? If yes, can you upload it to somewhere I can download from without requiring registration?
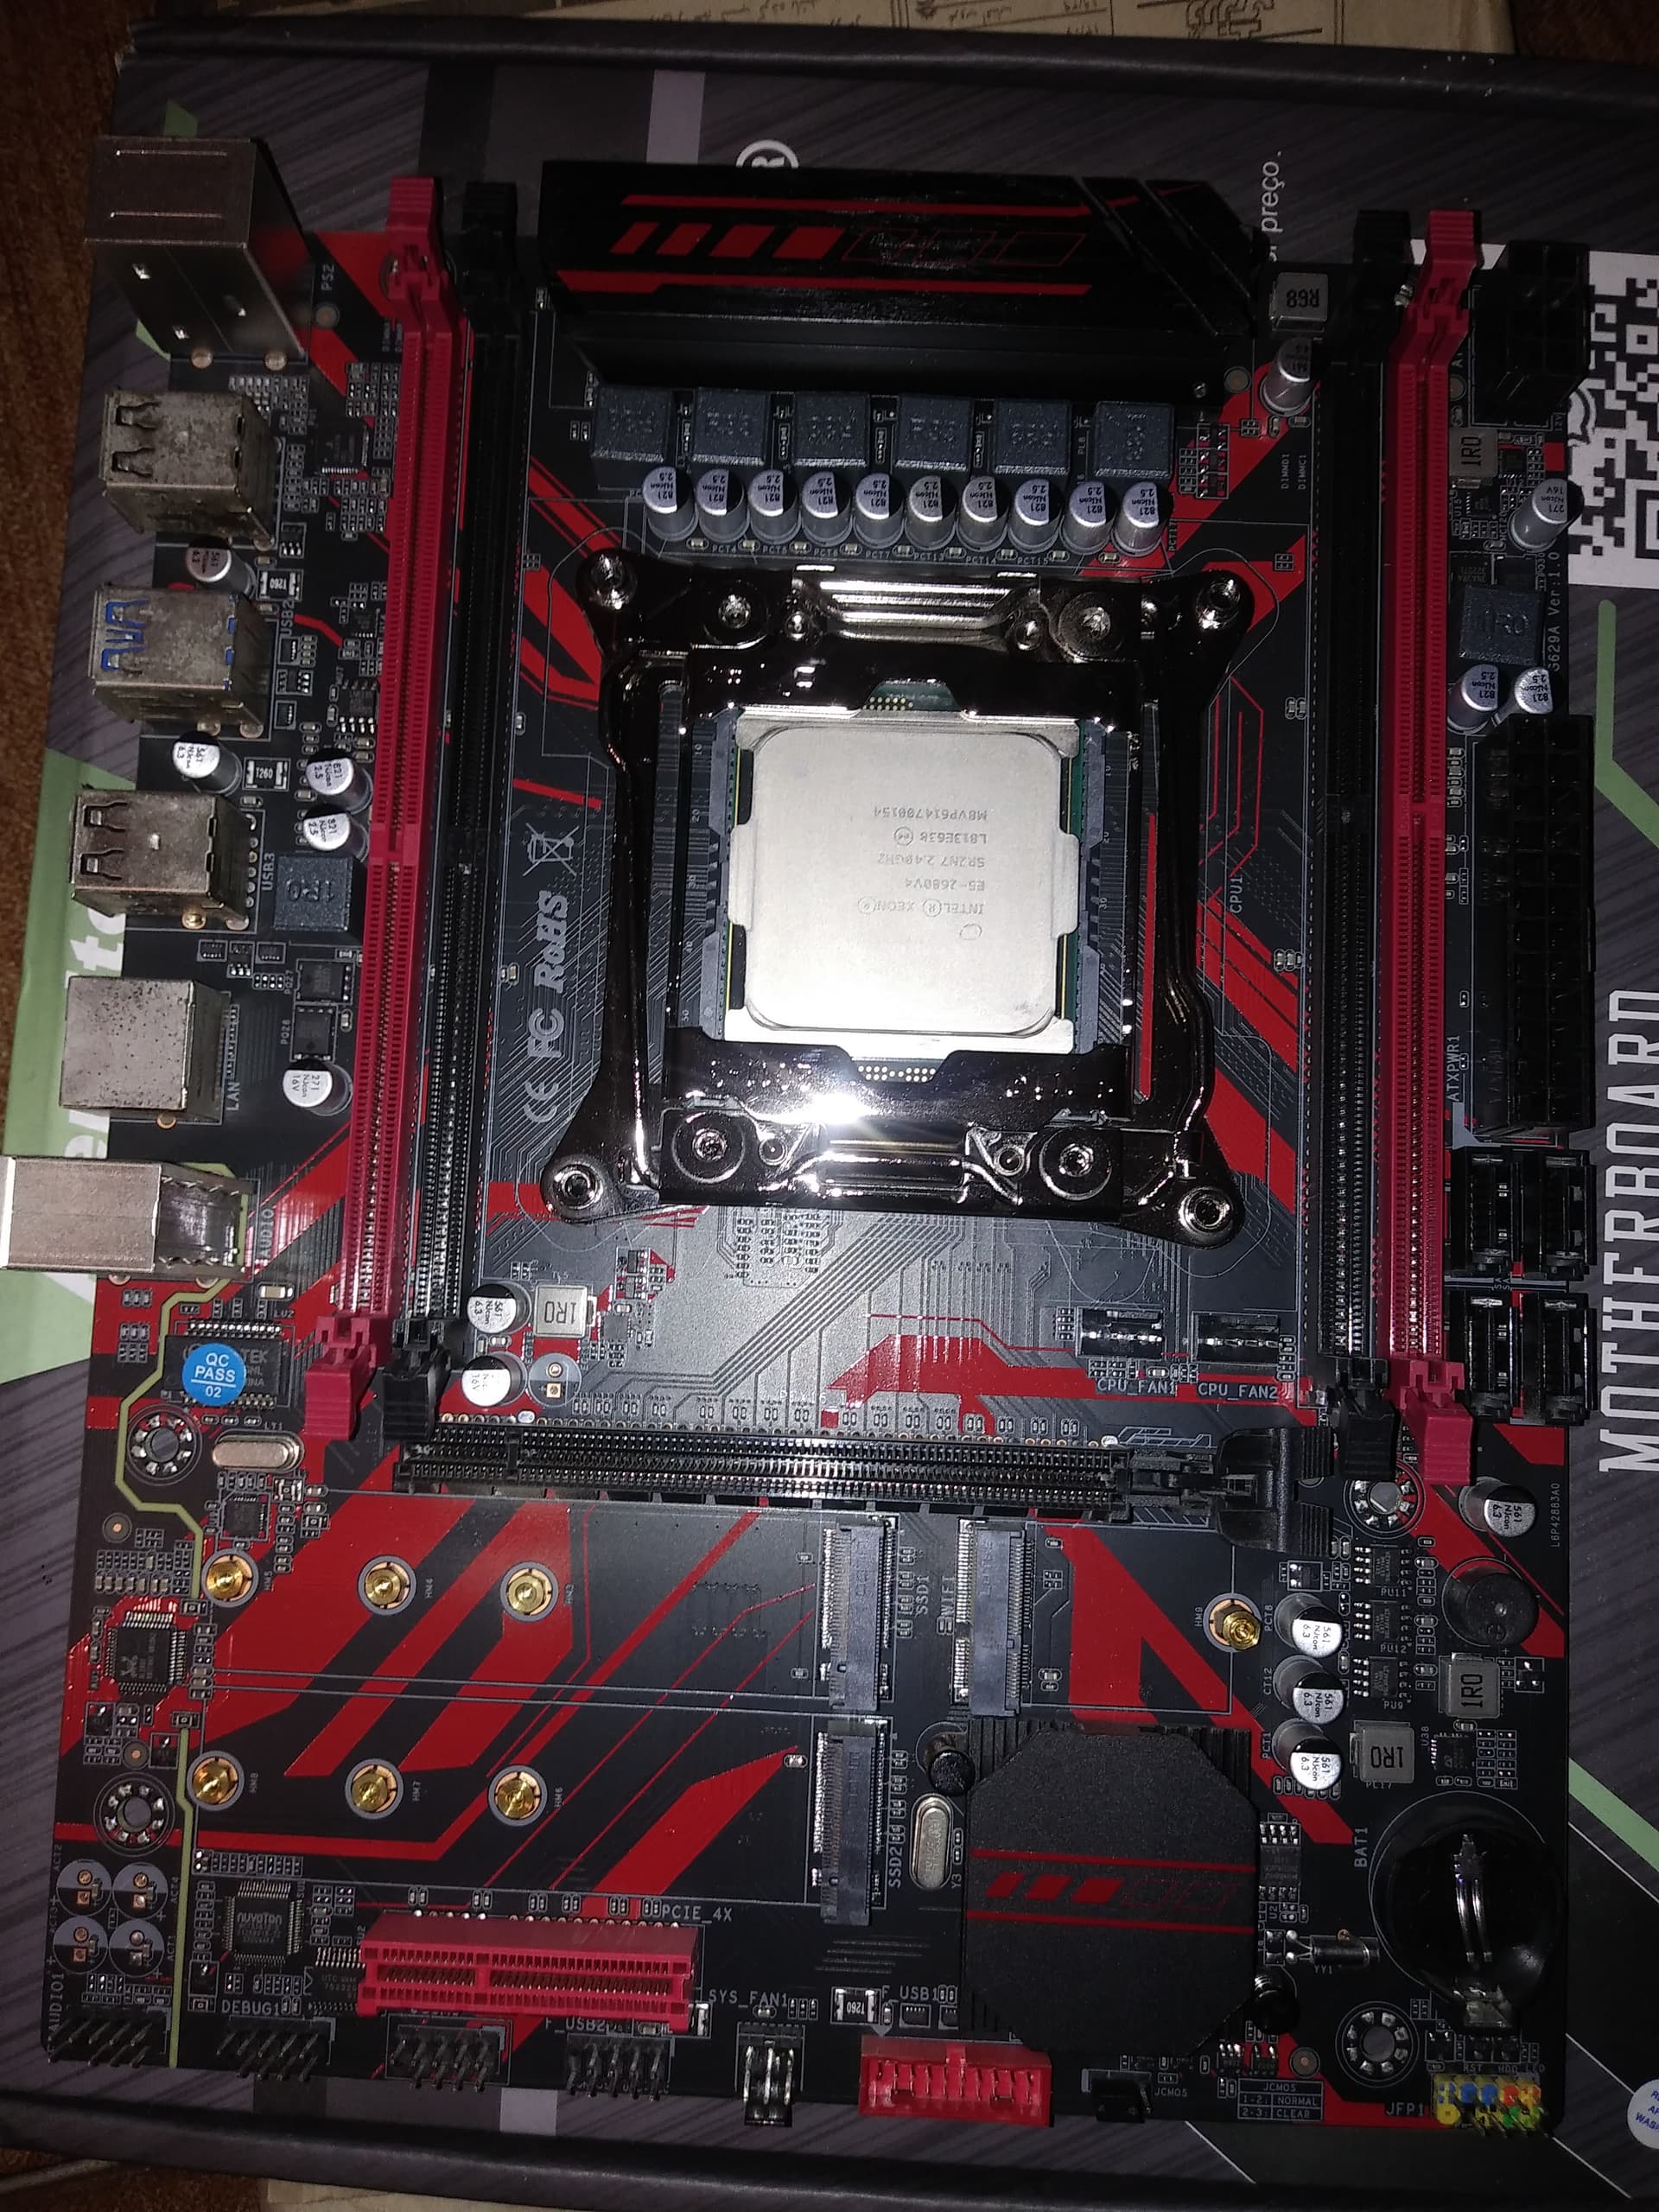
Do you have a picture showing the entire motherboard, not just the Debug port area?
How long ago did you buy this board?
I checked further with FITC, and it also shows me that the ME region (9.1.30) is configured for a B85 chipset. Which is good news on the whole, it is just “Example 4” when putting together a BIOS.
Edit: ME region was configured exactly the same between the 2022 and the 2024 version. Which is expected.
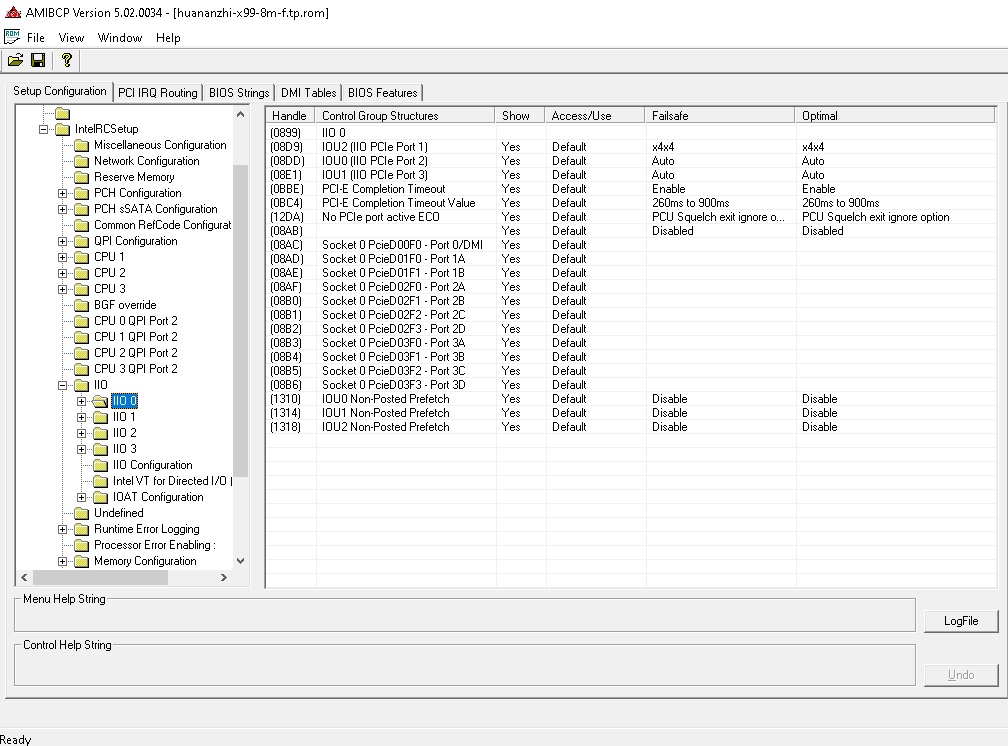
Basically just follow the original G629A BIOS (not 8M-F), including ME and IIO 0 configuration. In my own experience with 8 types of motherboards, that works without any problem.
Also make sure that you have a new enough GPU that supports UEFI booting. This is a common requirement on any BIOS on any platform, the moment you enable Secure Boot.
I have a Machinist X99 PR9-H (black PCB) and I’m trying to get TPM 2.0 + Secure Boot working, because Valorant (Vanguard) requires both on Windows 11.
My board:
Board: MACHINIST X99 PR9-H (black PCB)
BIOS: AMI 5.11, dated 02/22/2024
Super I/O: Nuvoton NCT6779D (per HWiNFO)
CPU: Xeon E5-2650 v4, GPU: GTX 1660
Windows 11 24H2, UEFI boot already working (GPT)
Flash chip: [marking on the 8-pin chip]
TPM header: [JLPC1 / DEBUG, pins soldered or not]
Problems:
The BIOS has no Secure Boot option.
Setting CSM to Disabled freezes the BIOS.
No TPM module installed yet.
I found the modded BIOS “X99 PR9 v1.4 (by FIB)” from tiburcillo’s post, but its internal ID says “MACHINIST X99 PR9”, not PR9-H, and I’m worried about hardware differences (chipset, flash chip, Super I/O).
Questions:
Has anyone tested this BIOS (or any other mod) on a PR9-H or PR9-H 2.0?
Is there a PR9-H specific BIOS with Secure Boot?
I read that the official PR9-H BIOS already supports TPM. Can anyone confirm?
How can I tell which chipset (H81/Q85/Q87) my PR9-H has?
I have a CH341A programmer and will make two dumps of my current BIOS before flashing anything. Thanks!
Can you start by uploading a complete 16M copy of your original BIOS to somewhere I can download from without requiring registration?
From what I can remember the PR9-H board is HM55 based, which means I personally have no way of helping you here. No experience. If you have problems, I would simply try looking through the Angxun BIOS page.
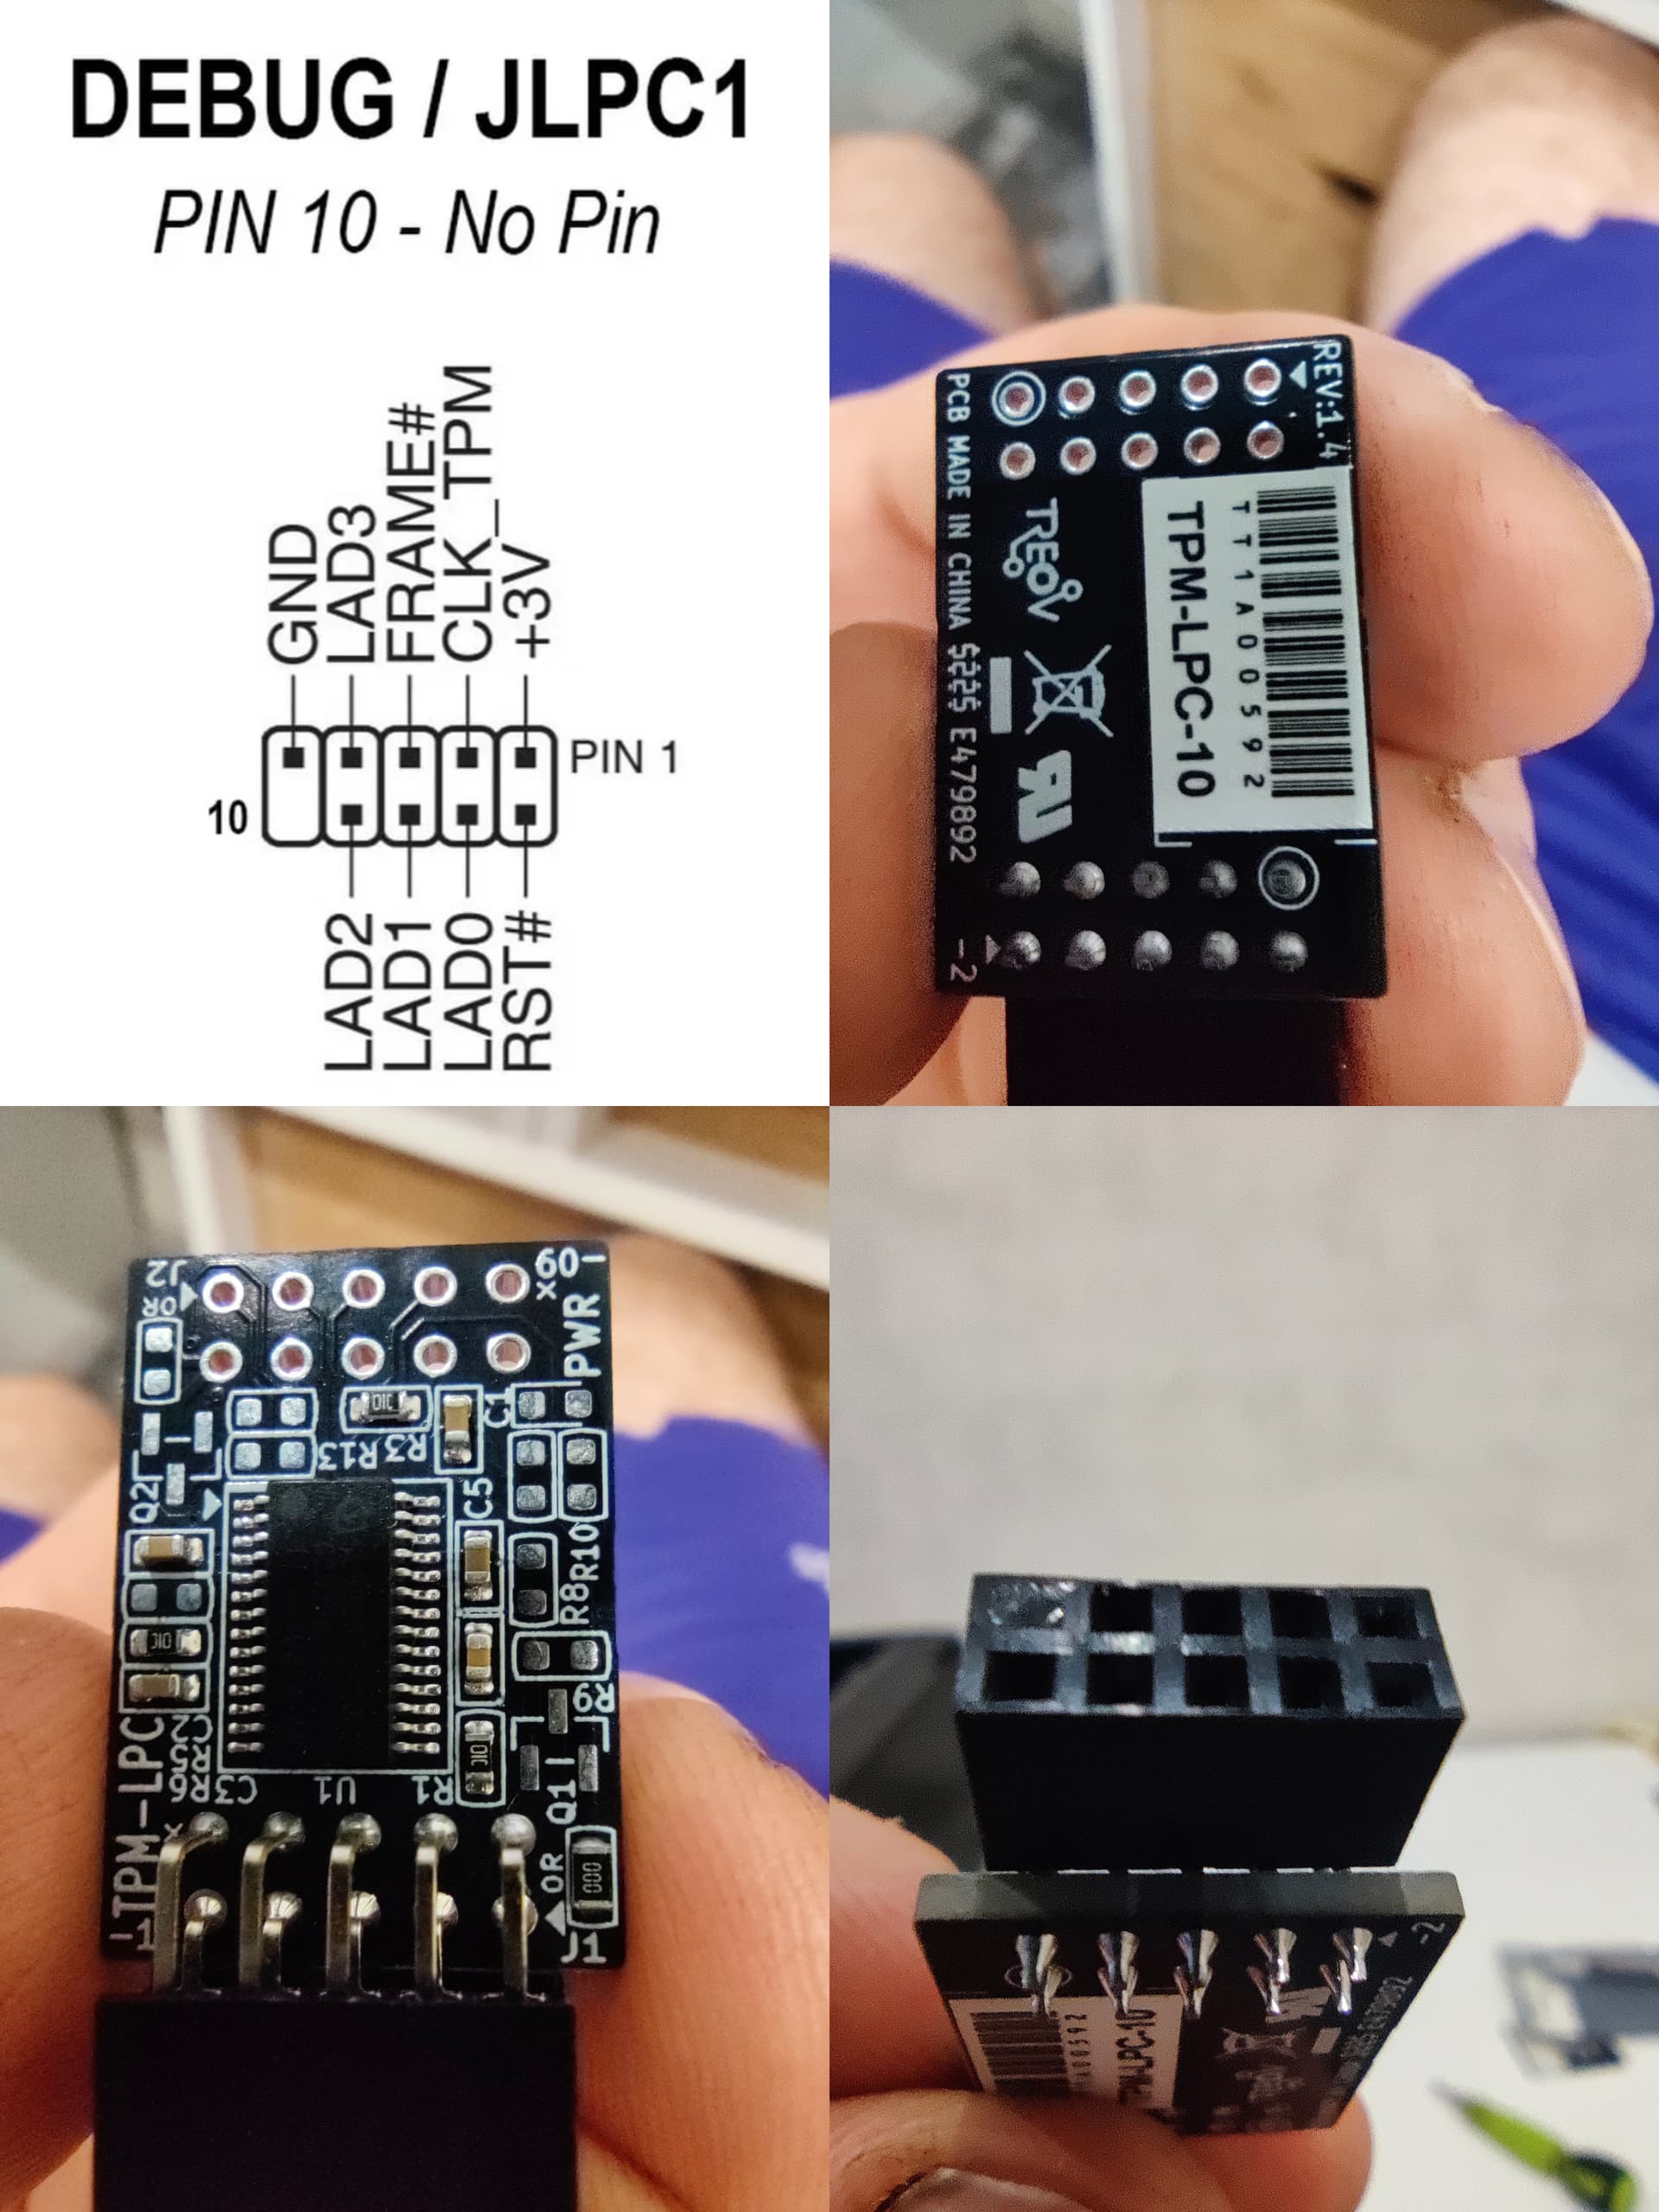
Hello there, good afternoon. I appreciate in advance your contribution regarding the X79 and X99 platforms and the lack of TPM 2.0 support. You see, I have a Machinist B9 X99 motherboard; it has a section at the bottom labeled “DEBUG,” and I assume that is where the connection pins for an external TPM 2.0 module should go. I would like to know where to start and what tools or materials I need to add TPM 2.0. Thank you for what you do; also, if it’s not too much to ask, could you please keep the explanation simple? I tend to get a bit lost in this conversation thread.
Yes, I’ve read that section thoroughly; I just have a few questions. Which exact TPM 2.0 model should I use? How should I solder the wires? And what is the diagram’s orientation? I assume it’s based on the board’s natural position
Earlier I gave up completely on the older Huananzhi motherboards. I made some test BIOSes, but I did not receive any usable feedback. Anyhow:
For 5532 based boards like in your case, then the BIOS in this post seems to work well. See confirmation from the user brichanfiana in the post below that one
My recommendations having done this twice on a X99D3M4 and X99D4M4
Buy a TPM module that has 2.54mm pitch width. That is typically sold as a 20-pin generic TPM module on Taobao/Aliexpress/Ebay etc
Do not solder any wires on the motherboard. Instead solder on pins on the unpopulated header. In particular, I bought several 5*1 rows of 2.54mm pins. Then installation is exactly the same as any other board. You can also use the header with a debug card, as I show in the second post in this thread
The diagram is oriented “as you see it”. If unsure what that means, there are multiple ground points (GND) on the TPM module. You can put the multi-meter in continuity/beep mode to clarify things
Back when I first installed the TPM, it was a 2mm-pitch model, so I had to make an adapter cable, but nowadays you can get TPMs that plug in directly from sites like AliExpress. It’s still working on Windows Server Insider Canary, including Secure Boot. I’ll post the old screenshot again here. (The driver for the ASR-81605ZQ I’m using isn’t up to scratch, so if I run programmes like HWInfo, the RAID stops working, which means I can’t take screenshots straight away.)
This is an English speaking forum, so please use English. On a personal level I do not speak Russian or Portuguese, but I use translation tools to get information.
In my experience, B7 typically means that the BIOS flash chip is not supported. So what flash chip are you using? In particular, what is the SPI ID when you detect it with for instance NeoProgrammer?
Ok, then I think this really drives home the point about my lack of understanding the difficulties with the F8/T8/TF BIOS compatibility. Proposed way forward: